CMS API Hub Power Your Stack with CMS, APIs & Payments

CMS API Hub

Power Your Stack with CMS, APIs & Payments

Latest Articles

Clocks Out of Sync: How Timestamp Fragmentation Across Your CMS and Payment Stack Makes Reconciliation Mathematically Impossible
Payment Processing

Clocks Out of Sync: How Timestamp Fragmentation Across Your CMS and Payment Stack Makes Reconciliation Mathematically Impossible

When your CMS, API middleware, and payment processor each maintain independent notions of time, reconciliation does not merely become difficult—it becomes structurally unsolvable. This article examines how timezone inconsistencies, clock drift, and normalization failures compound into quarterly revenue discrepancies that no spreadsheet can close.
Schema Sprawl and the Quarterly Cost of Unmaintained CMS Field Definitions in Payment Pipelines
Content Management Systems

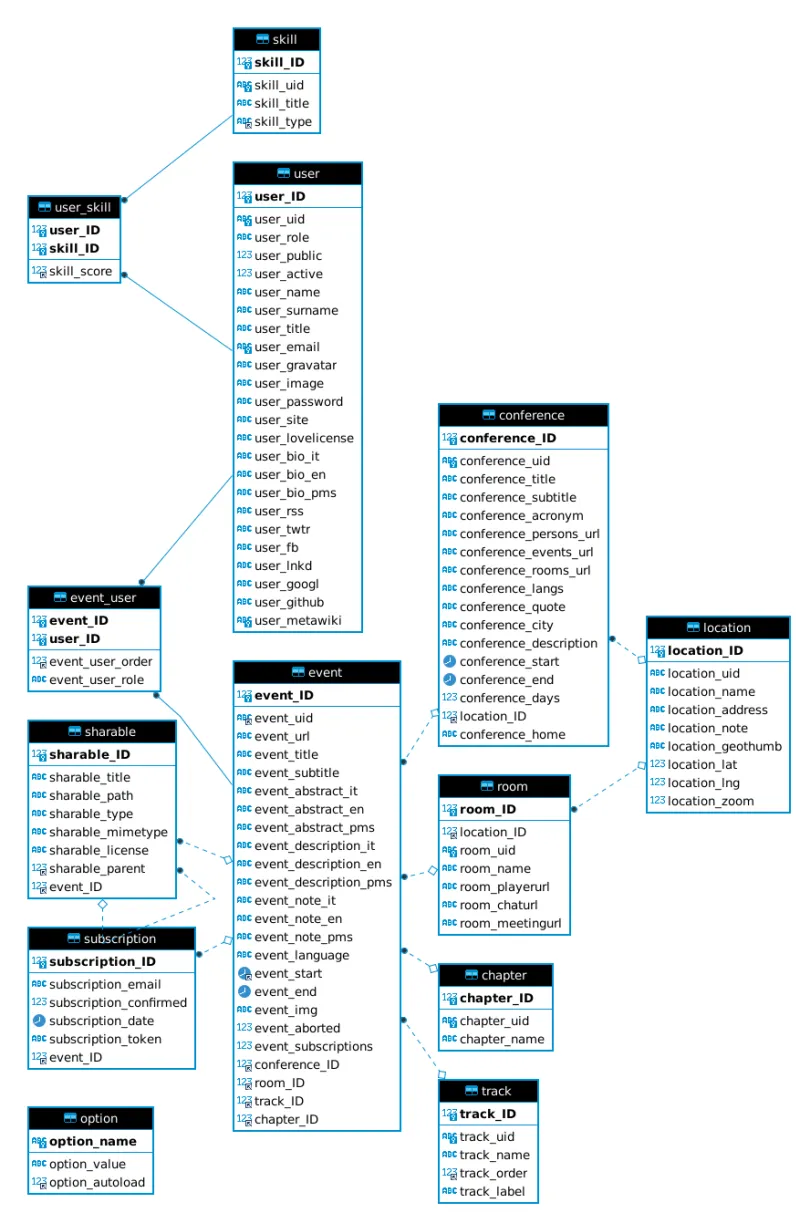
Schema Sprawl and the Quarterly Cost of Unmaintained CMS Field Definitions in Payment Pipelines

Every quarter that passes without deliberate field lifecycle governance adds another layer of complexity to your payment schema mapping. This article examines how unchecked CMS field proliferation creates versioning conflicts, slows transaction processing, and transforms routine debugging into multi-day investigations—then offers a structured governance framework to reverse the damage.

Webhook Logs as Legal Evidence: Building an Immutable Audit Trail That Wins Chargeback Disputes
Payment Processing

Webhook Logs as Legal Evidence: Building an Immutable Audit Trail That Wins Chargeback Disputes

When a customer disputes a charge, your CMS webhook event logs may be the only authoritative record of what actually happened between your platform and the payment processor. Engineering teams that treat event logs as ephemeral debugging artifacts rather than forensic assets routinely lose winnable chargeback cases. This article examines how to architect logging infrastructure that holds up under scrutiny—and why the difference between a log and a legally credible audit trail is more consequenti

The Real Price of 'At Least Once': What Webhook Delivery Guarantees Are Actually Costing Your Engineering Team
Payment Processing

The Real Price of 'At Least Once': What Webhook Delivery Guarantees Are Actually Costing Your Engineering Team

Webhook delivery guarantees sound like a solved problem until you start counting the engineering hours, storage overhead, and infrastructure complexity required to handle them correctly. This analysis breaks down the hidden operational costs embedded in 'at least once' delivery semantics and examines whether upgrading to a more reliable provider is the more economical path forward.

Payment Processing

Configuration Changes Nobody Recorded: The Hidden Compliance and Revenue Risk in Your CMS Payment Settings

When a payment configuration change goes unlogged in your CMS, you lose far more than a timestamp—you lose the ability to reconstruct what happened, who authorized it, and when things broke. This article examines the operational and compliance costs of inadequate audit trails across CMS, API, and payment processor layers, and offers a practical framework for closing those gaps before regulators or chargebacks do it for you.

When Numbers Lie: How CMS Field Type Mismatches Silently Corrupt Your Payment Amounts
Payment Processing

When Numbers Lie: How CMS Field Type Mismatches Silently Corrupt Your Payment Amounts

Subtle incompatibilities between CMS field types and payment processor data schemas can corrupt transaction amounts, tax calculations, and currency conversions at scale without triggering a single error log. Rounding errors, floating-point drift, and implicit type coercion compound quietly across thousands of transactions before they surface as unreconcilable ledger gaps. This article examines how these mismatches originate, how they propagate, and how to audit your stack before the damage becom

Compliance Theater: Why Your Payment Audit Trail Disappears Between CMS, API, and Processor Layers
Payment Processing

Compliance Theater: Why Your Payment Audit Trail Disappears Between CMS, API, and Processor Layers

Many organizations operate under the assumption that passing a PCI DSS self-assessment questionnaire means their transaction flows are fully auditable. In practice, the logging gaps that exist between CMS platforms, custom APIs, and payment processors create compliance blind spots that neither internal teams nor external auditors can reliably reconstruct. This article examines where those gaps form, why they persist, and how to architect genuine end-to-end auditability without a full-stack rewri

Partial API Failures and the Inventory-Payment Divergence That Quietly Breaks Your Books
Payment Processing

Partial API Failures and the Inventory-Payment Divergence That Quietly Breaks Your Books

When a payment API call succeeds but the downstream inventory update fails, your systems enter a state of silent disagreement that compounds into financial and operational chaos. This article examines the mechanics of transactional divergence across CMS, payment processor, and inventory layers—and offers a diagnostic framework for catching state mismatches before they reach your auditors.

Invisible Losses: How Webhook Timeout Cascades in Payment APIs Quietly Drain Your Transaction Revenue
Payment Processing

Invisible Losses: How Webhook Timeout Cascades in Payment APIs Quietly Drain Your Transaction Revenue

Webhook timeout failures in payment integrations are among the most underdiagnosed sources of silent revenue loss in modern digital commerce. When your CMS and payment processor fail to complete event handshakes within configured thresholds, orders vanish without a trace—and your logs rarely tell the full story. This article examines the mechanics of timeout cascades, how to surface them in your infrastructure, and what it takes to build resilient webhook pipelines that protect every transaction

Ghost in the Stack: The True Cost of Orphaned Webhook Subscriptions Draining Your CMS Infrastructure
Content Management Systems

Ghost in the Stack: The True Cost of Orphaned Webhook Subscriptions Draining Your CMS Infrastructure

Orphaned webhook subscriptions and abandoned event handlers quietly accumulate inside enterprise CMS environments, consuming compute resources, widening attack surfaces, and inflating operational budgets with zero business return. Understanding how these ghost integrations form—and how to systematically eliminate them—is one of the most underappreciated maintenance disciplines in modern content and payment infrastructure management.

Order History vs. Payment Ledger: Diagnosing the Silent Drift Destroying Your Reconciliation Workflow
Payment Processing

Order History vs. Payment Ledger: Diagnosing the Silent Drift Destroying Your Reconciliation Workflow

When your CMS order records and payment processor ledger refuse to agree, the cause is rarely a single bug—it is a systemic collision of incompatible timestamp standards, divergent state machines, and conflicting retry logic. This article examines the structural reasons reconciliation fails at scale and offers a diagnostic framework for determining which system deserves source-of-truth authority in multi-platform architectures.

What Backward Compatibility Actually Costs: The Hidden Economics of Payment API Schema Versioning
Payment Processing

What Backward Compatibility Actually Costs: The Hidden Economics of Payment API Schema Versioning

Maintaining backward compatibility across payment API schema versions feels like a safe, conservative choice—until the accumulated engineering debt starts showing up on your balance sheet. This analysis examines the compounding operational costs of legacy field support, deprecated enum values, and transitional data mappings that routinely push schema maintenance budgets three to five times beyond initial API development spend.

Garbage In, Declined Out: How Permissive CMS Validation Is Quietly Poisoning Your Payment Pipeline
Payment Processing

Garbage In, Declined Out: How Permissive CMS Validation Is Quietly Poisoning Your Payment Pipeline

When CMS field validation rules are too lenient—or absent entirely—malformed data flows unchecked into payment processors, triggering silent failures that compound over time. This article examines the architectural gaps that allow bad data to reach production, from missing email constraints to broken currency formats, and offers a concrete checklist for hardening your validation layer before it becomes a liability.

Broken Before It Arrives: How CMS Validation Gaps Corrupt Payment Data at Scale
Content Management Systems

Broken Before It Arrives: How CMS Validation Gaps Corrupt Payment Data at Scale

When content validation rules are incomplete or absent in headless CMS platforms, the consequences extend far beyond a missing field—they cascade into failed transactions, disputed charges, and regulatory exposure. This article examines how structural weaknesses in your CMS content model silently degrade payment data integrity, and offers a practical diagnostic framework for identifying vulnerabilities before they reach your processor.

Corrupted at the Source: How CMS Schema Failures Quietly Poison Your Payment Pipeline
Content Management Systems

Corrupted at the Source: How CMS Schema Failures Quietly Poison Your Payment Pipeline

When content validation breaks down inside a headless CMS, the damage rarely stays contained. This article examines how schema mismatches, missing fields, and type conflicts propagate silently through API layers until they surface as reconciliation nightmares inside your payment processor.

Countdown to Failure: The True Cost of Ignoring API Deprecation in Your Payment Infrastructure
Payment Processing

Countdown to Failure: The True Cost of Ignoring API Deprecation in Your Payment Infrastructure

Payment integrations rarely fail all at once—they erode quietly, endpoint by endpoint, until a deprecated API call triggers a mid-transaction error that costs far more than a proactive migration ever would have. Understanding how deprecation cycles function as a financial risk, not merely a technical inconvenience, is the first step toward building infrastructure that survives the inevitable. This article examines the hidden costs, early warning systems, and organizational frameworks that keep p

Idempotency Failures and Exponential Backoff Traps: How Webhook Retry Logic Is Corrupting Your Payment Reconciliation
Payment Processing

Idempotency Failures and Exponential Backoff Traps: How Webhook Retry Logic Is Corrupting Your Payment Reconciliation

Misconfigured webhook retry strategies silently introduce phantom transactions and duplicate payment records that can go undetected for months. This article examines how exponential backoff failures, idempotency key mismanagement, and conflicting event state between payment processors and CMS platforms compound into serious reconciliation errors—and what engineering teams can do to build retry mechanisms that hold up under real-world conditions.

What Sync Lag Actually Costs: Measuring the Business Damage of CMS-to-Payment Data Delays
Payment Processing

What Sync Lag Actually Costs: Measuring the Business Damage of CMS-to-Payment Data Delays

Eventual consistency sounds like an acceptable engineering trade-off until revenue starts disappearing at the seams between your CMS and payment processor. Sync delays that seem negligible in development routinely produce measurable financial damage in production environments. This article examines how to calculate that damage—and how to close the gap before it compounds.

When Systems Drift Apart: The Compounding Integration Failures Between Your CMS and Payment Processor
Payment Processing

When Systems Drift Apart: The Compounding Integration Failures Between Your CMS and Payment Processor

As CMS platforms and payment processors evolve on independent release cycles, the integrations binding them together quietly degrade. Schema changes, renamed fields, and shifting business logic accumulate into failures that are rarely catastrophic but consistently expensive. This article examines how API drift materializes in production environments and offers a structured approach to detecting it before revenue suffers.

Grading Your Event Pipeline: A Structured Framework for Evaluating Webhook Reliability Across CMS and Payment Platforms
Content Management Systems

Grading Your Event Pipeline: A Structured Framework for Evaluating Webhook Reliability Across CMS and Payment Platforms

Vendor uptime claims rarely tell the full story of webhook delivery performance, and engineering teams frequently discover reliability gaps only after committing to a platform migration. This article provides a metrics-based scoring framework that allows teams to objectively benchmark their CMS and payment provider's event delivery capabilities against established industry standards—before the contract is signed.